> For the complete documentation index, see [llms.txt](https://cianciustyles.gitbook.io/everything-i-know/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://cianciustyles.gitbook.io/everything-i-know/s/security/ctfs.md).
# CTFs
## Cheat Sheets
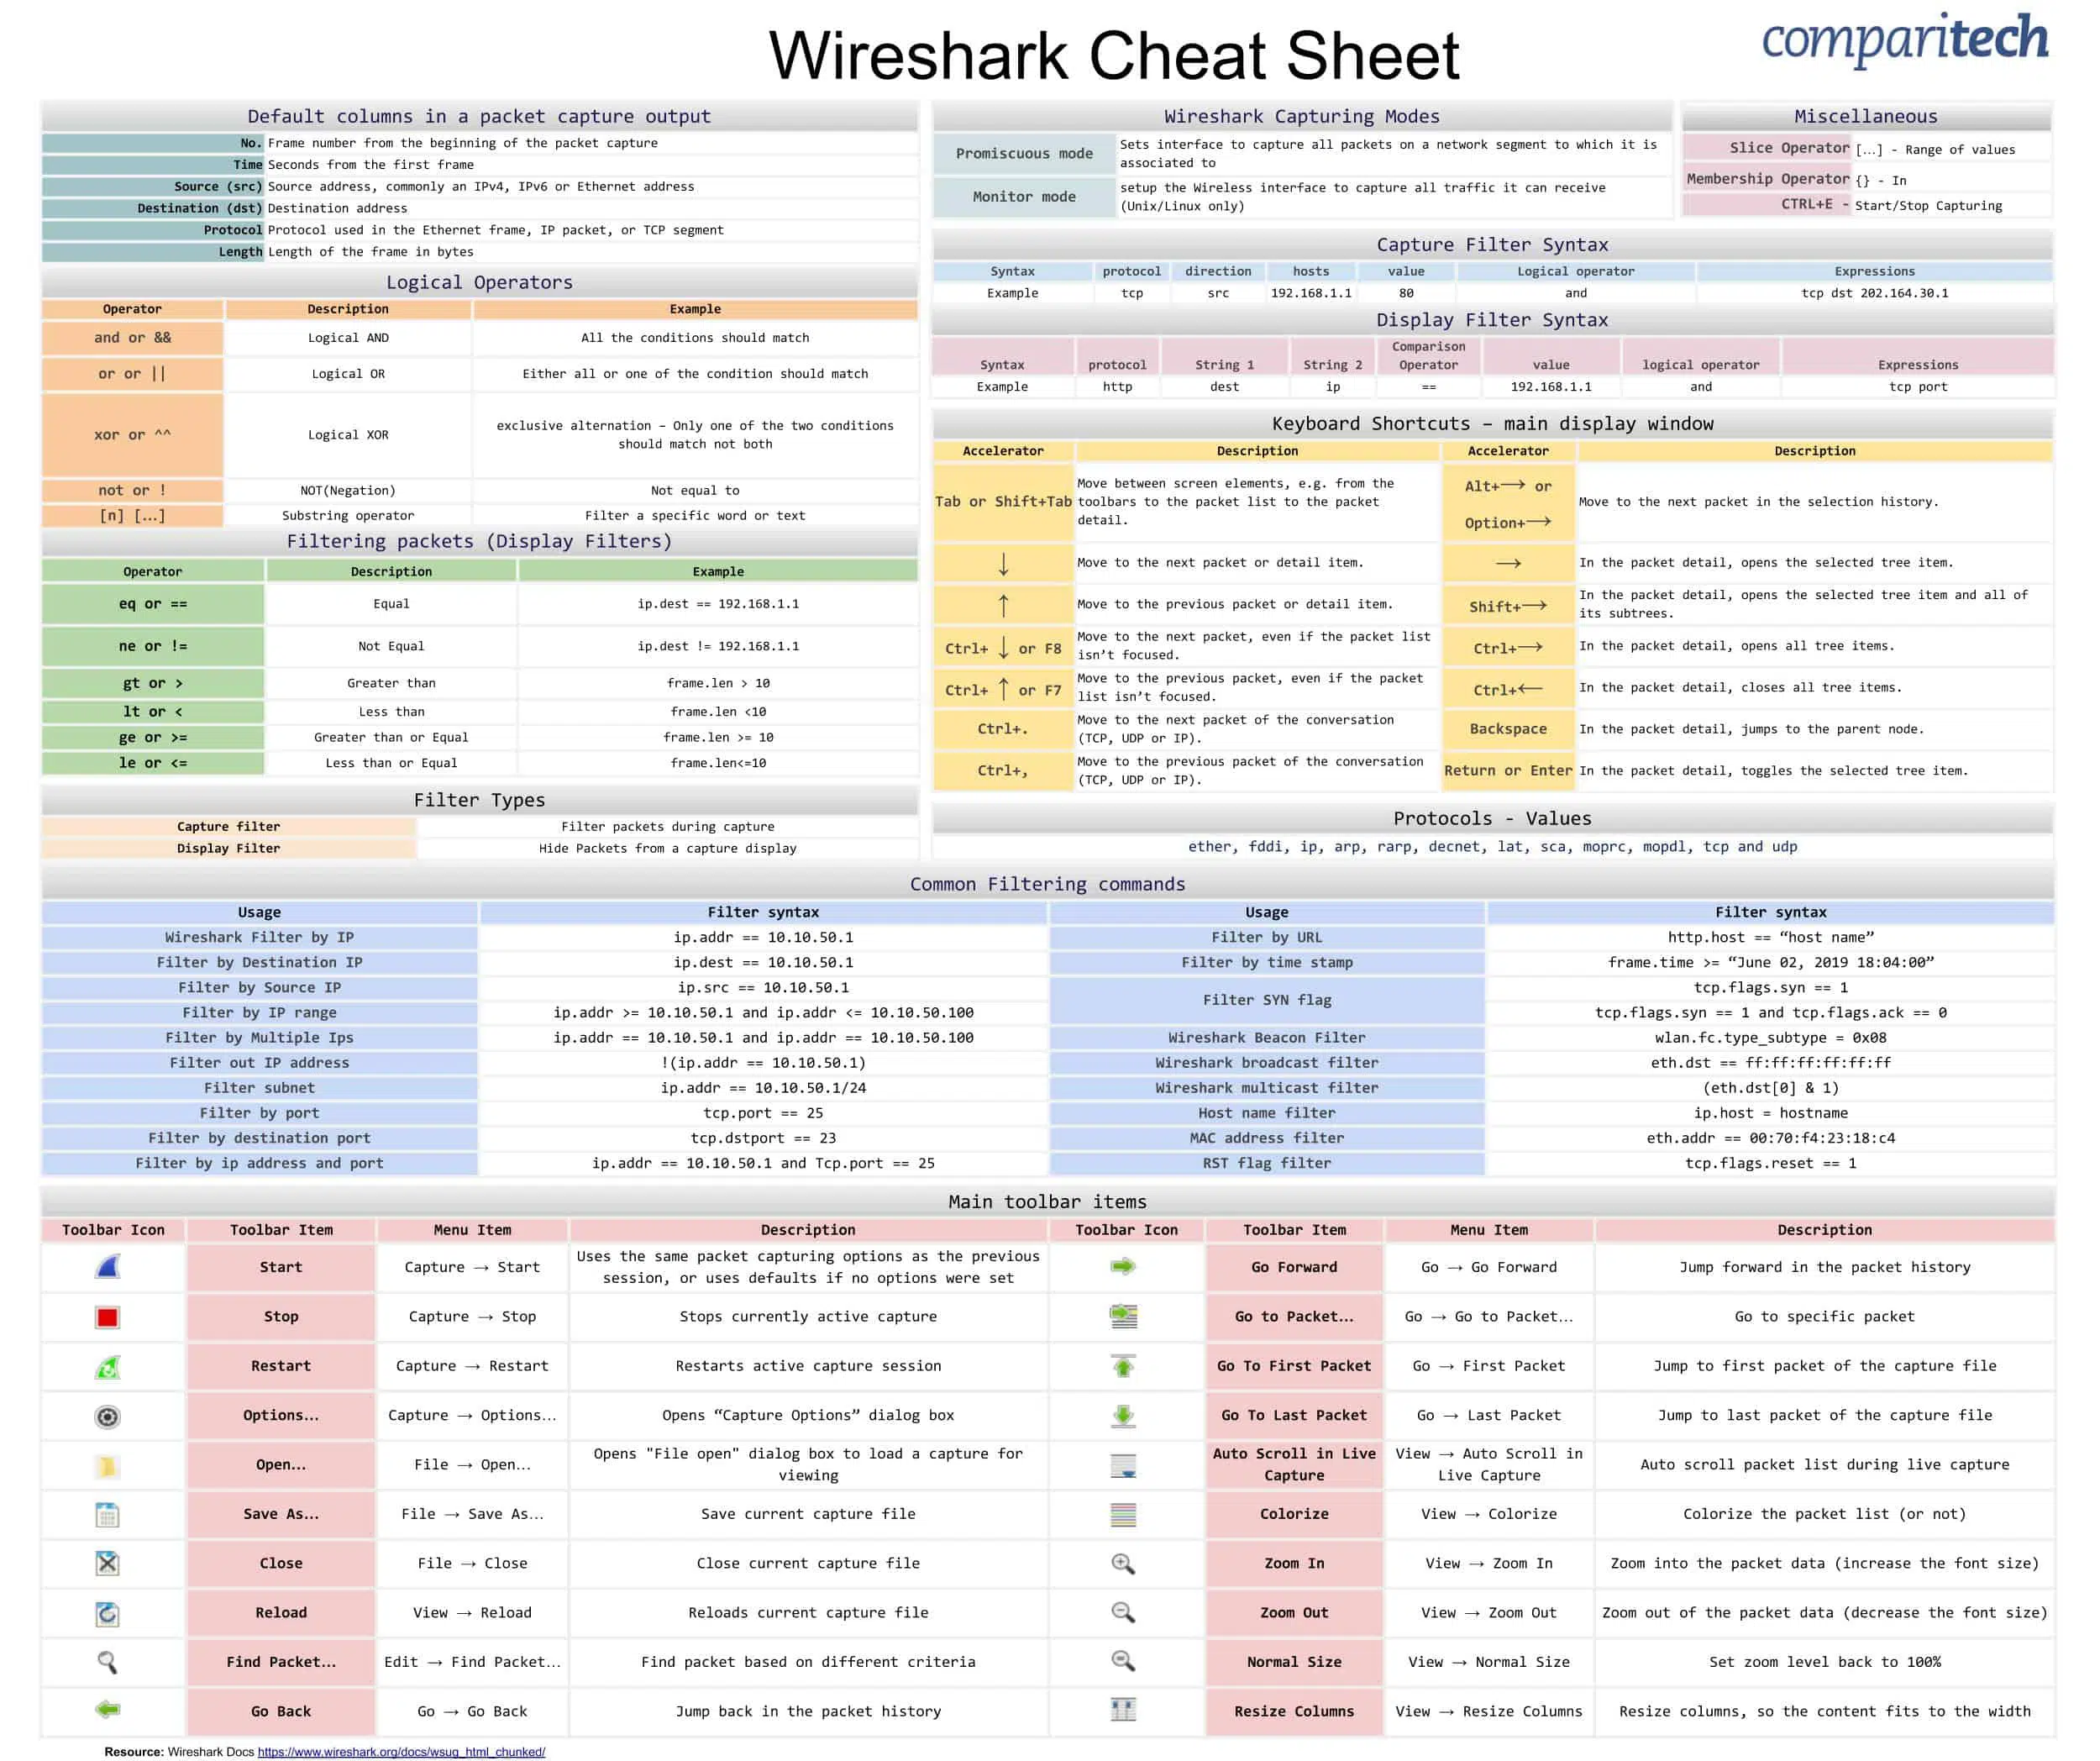
Wireshark Cheat Sheet
## Resources
### Articles
* [Bypassing file upload filter using .htaccess file](https://infosecwriteups.com/bypassing-file-upload-filter-using-htaccess-file-ctf-ca06d7e9ebd7) - Rahul Bogar
* [Capture The Flag (CTF) Resources For Beginners](https://medium.com/technology-hits/capture-the-flag-ctf-resources-for-beginners-9394ee2ea07a) - Abdul Issa
* [CTF Design Guidelines](https://bit.ly/ctf-design)
* [CTF Field Guide](https://trailofbits.github.io/ctf/)
* [CTF Resources](https://ctfs.github.io/resources/)
* [CTF Wiki](https://ctf-wiki.mahaloz.re/)
* [Escaping the PyJail](https://lbarman.ch/blog/pyjail/) - Ludovic Barman
* [HackTricks](https://book.hacktricks.xyz/welcome/readme) - Carlos Polop
* [Infosec Tools](https://shellsharks.com/infosec-tools)
* [Offensive Security Cheatsheet](https://cheatsheet.haax.fr/)
* [Online IT/Security Training](https://shellsharks.com/online-training)
* [Online Tools to crack CTF Contests](https://dhanumaalaian.medium.com/online-tools-to-crack-ctf-contest-1ad7efa958da)
* [picoCTF Primer](https://primer.picoctf.com/)
* [pwny.cc](https://www.pwny.cc/)
* [The Many Maxims of Maximally Effective CTFs](https://web.archive.org/web/20201124033521/https://captf.com/maxims.html)
### GitHub repositories
*
* [apsdehal/awesome-ctf](https://github.com/apsdehal/awesome-ctf)
* [CTFs](https://github.com/ctfs)
* [devploit/ctf-awesome-resources](https://github.com/devploit/ctf-awesome-resources)
* [Hacking Lab](https://github.com/onealmond/hacking-lab)
* [how2heap](https://github.com/shellphish/how2heap/)
* [RsaCtfTool](https://github.com/RsaCtfTool/RsaCtfTool) - retreive private key from weak public key and/or uncipher data
* [rsatool](https://github.com/ius/rsatool) - rsatool can be used to calculate RSA and RSA-CRT parameters
* [RSHack for CTF](https://github.com/zweisamkeit/RSHack) - Tool for RSA CTF's challenges
* [Security Cheat Sheet](https://github.com/security-cheatsheet)
* [CMD](https://github.com/security-cheatsheet/cmd-command-cheat-sheet)
* [Metasploit](https://github.com/security-cheatsheet/metasploit-cheat-sheet)
* [Reverse Shell](https://github.com/security-cheatsheet/reverse-shell-cheatsheet)
* [Wireshark](https://github.com/security-cheatsheet/wireshark-cheatsheet)
* [zardus/ctf-tools](https://github.com/zardus/ctf-tools)
### Offline Tools
* [ImHex](https://imhex.werwolv.net/)
#### Enumeration
* [AutoRecon](https://github.com/Tib3rius/AutoRecon)
* [FinalRecon](https://github.com/thewhiteh4t/FinalRecon)
* [nmapAutomator](https://github.com/21y4d/nmapAutomator)
* [Raccoon](https://github.com/evyatarmeged/Raccoon)
* [Reconbot](https://github.com/0bs3ssion/Reconbot)
* [RustScan](https://github.com/RustScan/RustScan)
* [Threader3000](https://github.com/dievus/threader3000)
#### Forensics
* [Aircrack-ng](https://www.aircrack-ng.org/) - assess WiFi security
* [bettercap](https://www.bettercap.org/) - perform reconnaissance and attack WiFi networks, Bluetooth devices and IPv4/IPv6 networks
* [capa](https://github.com/mandiant/capa) - identify capabilities in executable files
* [Detect It Easy](https://github.com/horsicq/Detect-It-Easy) - determines types of files
* [The Sleuth Kit](https://www.sleuthkit.org/) - analyse disk images and recover files
* [volatility](https://github.com/volatilityfoundation/volatility) - memory forensics
#### Networking
* [masscan](https://github.com/robertdavidgraham/masscan)
* [Nmap](https://nmap.org/)
* [Cheat sheet](https://www.stationx.net/nmap-cheat-sheet/)
* [Wireshark](https://www.wireshark.org/)
* [Zmap](https://zmap.io/)
#### Password Cracking
* [BruteX](https://github.com/1N3/BruteX)
* [hashcat](https://hashcat.net/hashcat/)
* [CrackerJack](https://github.com/ctxis/crackerjack) - Web GUI
* [GovCracker](https://github.com/Are-s-h/GovCracker)
* [hashcat.launcher](https://github.com/s77rt/hashcat.launcher) - cross-platform app that runs and controls hashcat
* [hate\_crack](https://github.com/trustedsec/hate_crack)
* [John the Ripper](https://www.openwall.com/john/)
* [Johnny](https://github.com/openwall/johnny) - GUI frontend
* [Ophcrack ](https://ophcrack.sourceforge.io/)- Windows password cracker
#### Reconnaissance
* [Bluto](https://github.com/darryllane/Bluto)
* [theHarvester](https://github.com/laramies/theHarvester)
#### Reverse Engineering
* [BARF ](https://github.com/programa-stic/barf-project)- Binary Analysis and Reverse engineering Framework
* [Boomerang ](https://github.com/BoomerangDecompiler/boomerang)- x86 to C decompiler
* [FLARE Obfuscated String Solver](https://github.com/mandiant/flare-floss) - extract and deobfuscate all strings from malware binaries
* [GDB](https://www.sourceware.org/gdb/) - GNU Debugger
* [GEF](https://github.com/hugsy/gef) - GDB Enhanced Features
* [pwndbg](https://github.com/pwndbg/pwndbg)
* [Ghidra](https://ghidra-sre.org/) - National Security Agency
* [IDA Pro](https://www.hex-rays.com/ida-pro/)
* [PLASMA ](https://github.com/plasma-disassembler/plasma)- x86/ARM/MIPS disassembler
### Online Tools
* [FastPeopleSearch](https://www.fastpeoplesearch.com/)
* [HexEd.it](https://hexed.it/)
#### Cryptography
* [CrackStation](https://crackstation.net/) - Online Password Hash Cracking
* [Password Cracking Dictionary (15 GB)](https://crackstation.net/crackstation-wordlist-password-cracking-dictionary.htm)
* [CrypTool-Online](https://www.cryptool.org/en/cto/)
* [dCode.xyz](https://www.dcode.fr/en)
* [factordb](http://factordb.com/)
* [Hash Decrypter](https://hashes.com/en/decrypt/hash)
* [Hash Type Identifier](https://hashes.com/en/tools/hash_identifier)
* [hashes.link](https://hashes.link/)
* [MD5Hashing.net](https://md5hashing.net/) - Hash, hashing and encryption toolkit
* [quipquip](https://www.quipqiup.com/)
* [Substitution cipher decoder](https://planetcalc.com/8047/)
* [Vigenère Solver](https://www.guballa.de/vigenere-solver)
#### Encoders / Decoders
* [CyberChef](https://gchq.github.io/CyberChef/)
* [Dencode](https://dencode.com/)
* [JSfuck Decoder](https://enkhee-osiris.github.io/Decoder-JSFuck/)
#### Forensics
* [InQuest Labs](https://labs.inquest.net/)
* [PacketTotal](https://packettotal.com/) - A free, online PCAP analysis engine
* [pcapfix](https://f00l.de/hacking/pcapfix.php) - online pcap / pcapng repair service
* [Simple Email Reputation](https://emailrep.io/)
* [VirusTotal](https://www.virustotal.com/) - Analyse suspicious files, domains, IPs and URLs to detect malware and other breaches
#### Reverse Engineering
* [androguard](https://github.com/androguard/androguard) - Android apps
* [apk2gold](https://github.com/lxdvs/apk2gold) - Android apps
* [Apktool](https://ibotpeaches.github.io/Apktool/) - Android apps
* [Java decompiler online](http://www.javadecompilers.com/)
* [Online Assembler and Disassembler](https://shell-storm.org/online/Online-Assembler-and-Disassembler/)
* [OnlineGDB](https://www.onlinegdb.com/)
* [Resource Hacker](http://www.angusj.com/resourcehacker/) - resource compiler/decompiler for Windows applications
* [ROPgadget](https://github.com/JonathanSalwan/ROPgadget)
#### Steganography
* [Aperi'Solve](https://www.aperisolve.com/)
* [StegCracker](https://github.com/Paradoxis/StegCracker)
* [stegextract](https://github.com/evyatarmeged/stegextract)
* [Steghide](https://steghide.sourceforge.net/)
* [Stegsolve](https://wiki.bi0s.in/steganography/stegsolve/)
* [zsteg](https://github.com/zed-0xff/zsteg/)
#### Web Exploitation
* [Burp Suite](https://portswigger.net/burp) - web application security testing
* [Commix](https://commixproject.com/) - command injection exploitation tool
* [dirsearch](https://github.com/maurosoria/dirsearch)
* [fimap](https://github.com/kurobeats/fimap) - local/remote file injection audit tool
* [gobuster](https://github.com/OJ/gobuster) - directory/file, DNS and VHost enumeration
* [goWAPT](https://github.com/dzonerzy/goWAPT)
* [Nikto](https://github.com/sullo/nikto) - web server scanner
* [Raccoon](https://github.com/evyatarmeged/Raccoon) - vulnerability scanner
* [Reverse Shell Generator](https://www.revshells.com/)
* [sqlmap](https://sqlmap.org/) - automatic SQL injection tool
* [SSL Server Test](https://www.ssllabs.com/ssltest/analyze.html)
* [w3af](https://w3af.org/) - web application attack framework
* [wfuzz](https://github.com/xmendez/wfuzz)
* [XSSer](https://xsser.03c8.net/) - cross site scripter
### Websites
* [247CTF](https://247ctf.com/)
* [316ctf](https://play.316ctf.com/) - Anderson University
* [CTFlearn](https://ctflearn.com)
* [CTFtime.org](https://ctftime.org/)
* [CTF Sites](https://ctfsites.github.io/)
* [Cyber Security Challenge Germany (CSCG)](https://play.cscg.live/)
* [Exploit Education](http://exploit.education/)
* [exploit-exercises.com](https://exploit-exercises.com/)
* [Google CTF](https://capturetheflag.withgoogle.com/beginners-quest)
* [hackArcana](https://hackarcana.com/)
* [Hacktoria](https://hacktoria.com/) - Story Driven OSINT CTF Events
* [ImaginaryCTF](https://imaginaryctf.org/) - Daily CTF Challenges for Everyone
* [Archived Challenges](https://imaginaryctf.org/ArchivedChallenges)
* [kCTF](https://google.github.io/kctf/) - Kubernetes-based infrastructure for CTF competitions
* [KITCTF](https://kitctf.de/)
* [MetaCTF](https://metactf.com/)
* [picoCTF](https://picoctf.org/)
* [Root Me](https://www.root-me.org/en/Challenges/)
* [The Flare-On Challenge](https://www.flare-on.com/)